PES web app
Users, groups and two-step sign-in
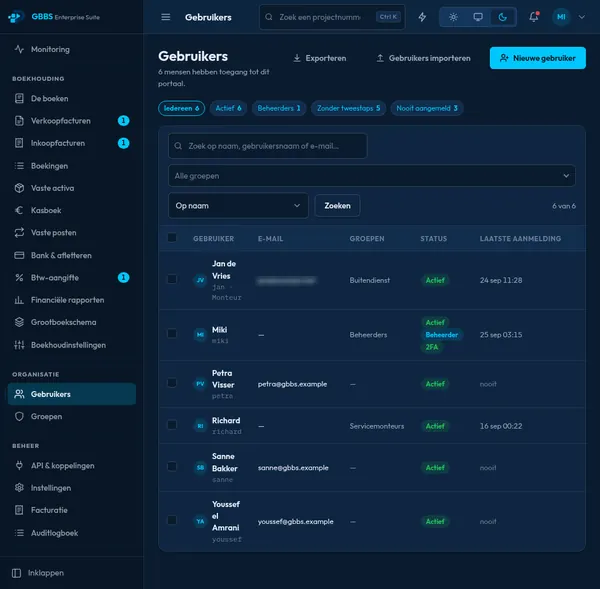
Filters show administrators, accounts without two-step verification and people who never signed in. Users are grouped, searchable and can be imported or exported.
How it works
Passwords are stored as Argon2id hashes and sessions are kept on the server, so an administrator can revoke one. Two-step verification uses standard time-based codes with recovery codes, passkeys use WebAuthn, and a company can require two-step for everyone. Users belong to groups that carry permissions. Accounts can be created in bulk from a spreadsheet, with a generated password sent by e-mail, or synced from Active Directory or LDAP, where people who leave are disabled rather than deleted. Every change is written to the audit trail.